Tomcat Vault
Enterprise Cryptographic Credential Manager, Diagnostic Verifier & DataSource Factory for Apache Tomcat Connection Pools.
🖼️ Visual Showcase & Highlights
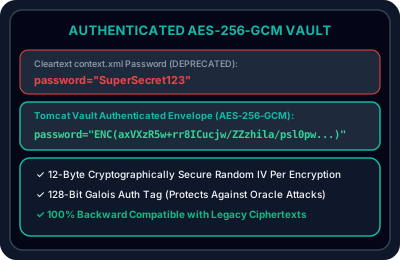
Enterprise-grade cryptographic credential manager, diagnostic verifier, and JNDI DataSource factory for Apache Tomcat connection pools. Eliminates cleartext database credentials from context.xml and server.xml using authenticated AES-256-GCM encryption, dynamic initialization vectors, pluggable key providers, cloud vault connectors, zero-downtime key rotation, and zero-leak logging.
Enterprise Infrastructure & Security Hardening

Uses 256-bit AES in Galois/Counter Mode (GCM) with 12-byte random IVs and 128-bit authentication tags. Adopts standard ENC(...) envelopes with key versioning tags while maintaining 100% backward compatibility for legacy hex/CBC ciphertexts.

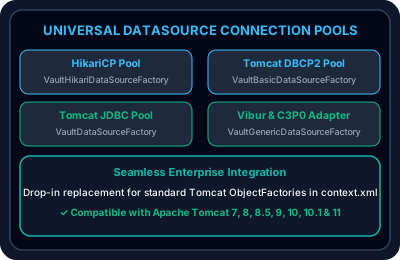
Dedicated high-performance DataSource factories for HikariCP (VaultHikariDataSourceFactory), Tomcat DBCP2 (VaultBasicDataSourceFactory), Tomcat JDBC (VaultDataSourceFactory), and Vibur DBCP / C3P0.

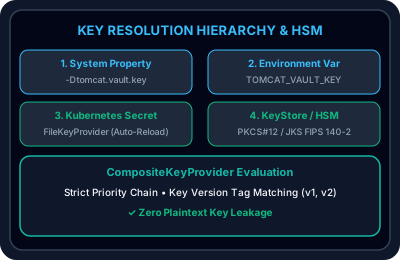
Hierarchical key resolution supporting System Properties, Environment Variables (TOMCAT_VAULT_KEY), Kubernetes secret auto-reload watchers, PKCS#12/JKS hardware keystores, and cloud providers.

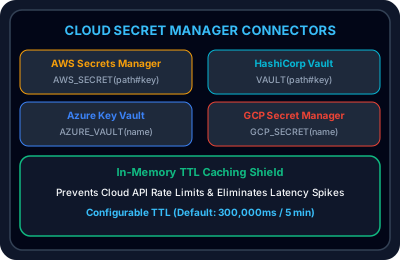
Dynamic credential resolution directly from AWS Secrets Manager (AWS_SECRET), HashiCorp Vault (VAULT), Azure Key Vault (AZURE_VAULT), and GCP Secret Manager with configurable TTL caching.

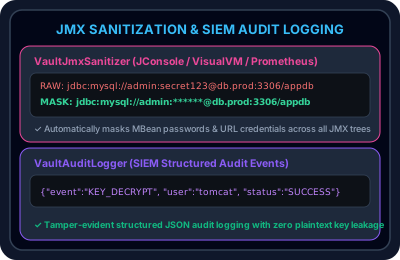
VaultJmxSanitizer automatically masks passwords and embedded URL credentials with ****** in JMX MBeans (JConsole, VisualVM, Prometheus). VaultAuditLogger provides structured SIEM audit events.

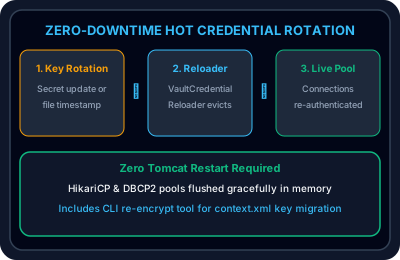
VaultCredentialReloader evicts stale connection pool instances and re-authenticates pool connections upon credential rotation without bouncing Tomcat. Includes in-place re-encryption CLI tooling.
🛠️ Pre-Flight Verification & Diagnostic CLI
Validate credentials and test live JDBC connections against context.xml before restarting production Tomcat.
java -jar tomcat-vault.jar --verify --context /opt/tomcat/conf/context.xmlInspect runtime JCE jurisdiction policy limits, cipher provider readiness, and PBKDF2 iteration speed.
java -jar tomcat-vault.jar --statusMasked interactive entry avoids leaving plaintext passwords in shell history or process tables.
java -jar tomcat-vault.jar -e🚀 JNDI Resource Configuration Examples
<Resource
    name="jdbc/AppDB"
    auth="Container"
    type="javax.sql.DataSource"
    factory="umrao.tomcat.vault.VaultHikariDataSourceFactory"
    driverClassName="com.mysql.cj.jdbc.Driver"
    jdbcUrl="jdbc:mysql://db.prod.internal:3306/appdb"
    username="app_user"
    password="ENC(axVXzR5w+rr8ICucjw/ZZzhila/psl0pw...)"
maximumPoolSize="20" /><Resource
name="jdbc/CloudDB"
auth="Container"
type="javax.sql.DataSource"
factory="umrao.tomcat.vault.VaultDataSourceFactory"
username="AWS_SECRET(prod/database#username)"
password="AWS_SECRET(prod/database#password)"
url="jdbc:mysql://db.prod.internal:3306/appdb" />📊 Quality Assurance & Test Metrics
⚡ Developer Quickstart & Source Access
This enterprise system tool is fully configured for cloud-native containerized execution (Podman, Docker, Helm) and local development workflows.